AWS Three-Tier Web Architecture
Slides + PowerPoint5 slides
Free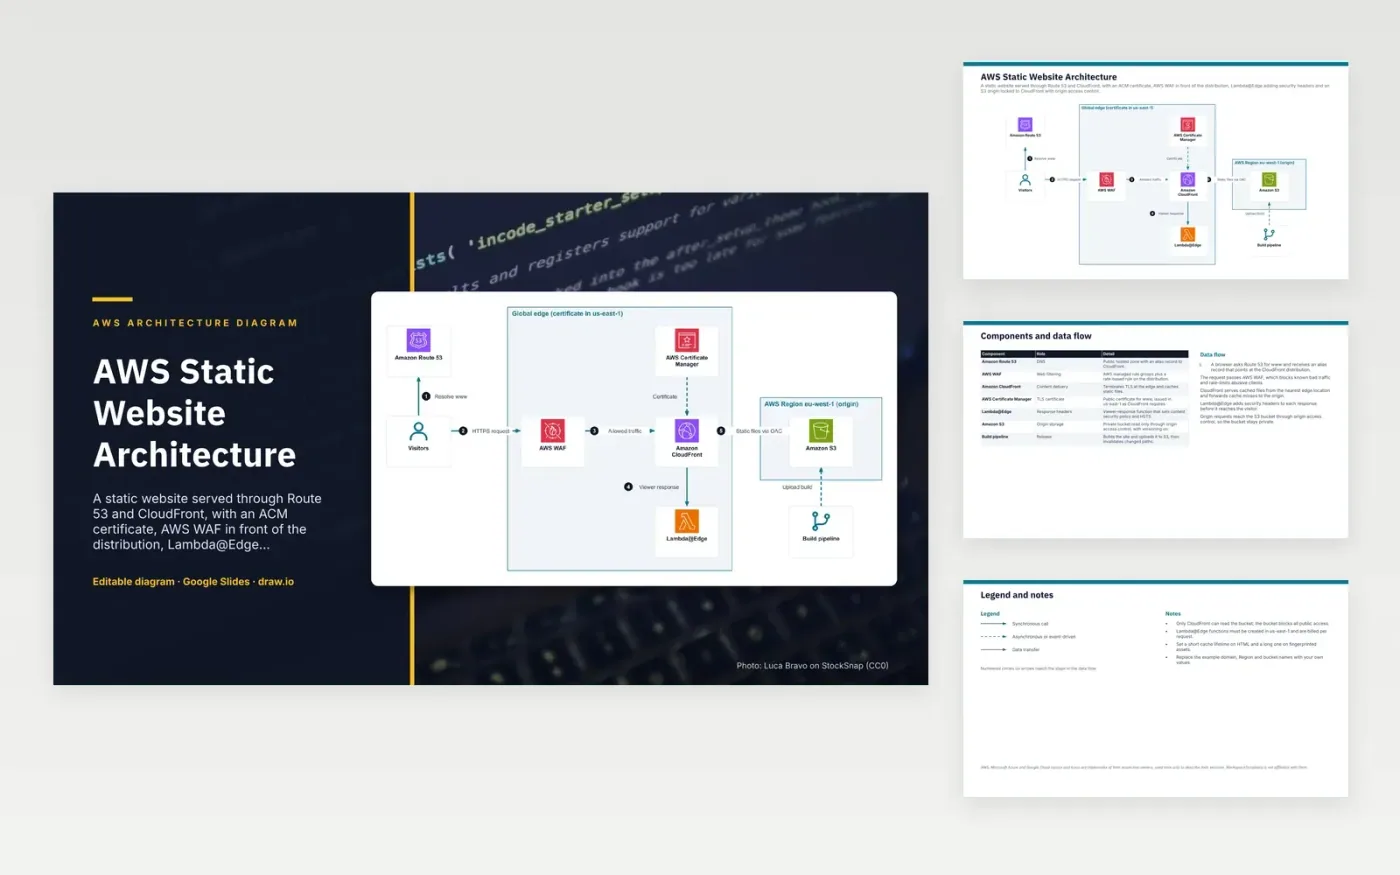
A browser resolves www through Amazon Route 53, which returns an alias record pointing at a CloudFront distribution. The request passes AWS WAF, which blocks known bad traffic and rate-limits abusive clients. CloudFront serves cached files from the nearest edge location. On the response, Lambda@Edge adds security headers before the file reaches the visitor. Cache misses go to the S3 bucket, which CloudFront reads through origin access control.
The bucket blocks all public access, so the only route to the files is CloudFront. A build pipeline uploads each release to S3 and invalidates the changed paths. Cache lifetimes are split: HTML gets a short one so updates appear quickly, and fingerprinted assets get a long one. Anyone adapting this should change the domain, Region and bucket names, and remember that the certificate and Lambda@Edge functions must be in us-east-1.
The diagram uses the official AWS architecture icons, each labelled with its service name. AWS, Microsoft Azure and Google Cloud names and icons are trademarks of their respective owners, used here only to describe their services. WorkspaceTemplates is not affiliated with them.
Click Make a copy in Google Slides, then confirm on the Google page. The copy is saved to your own Google Drive.
Rename Visitors, Amazon Route 53, AWS WAF and the other boxes inside Global edge (certificate in us-east-1) to your own components, and delete the ones your system does not have.
Rewrite the 5-step data flow and the 7-row components table so they match the arrows you keep.
For the draw.io version, download aws-static-website-architecture-diagram.drawio and open it at app.diagrams.net.
Origin access control lets only this CloudFront distribution read the bucket, and the bucket blocks all public access. Visitors reach the files only through CloudFront, so they cannot skip WAF or the response headers by using the bucket address.
CloudFront reads its TLS certificates from the US East (N. Virginia) Region only, so the ACM certificate has to be requested there. Lambda@Edge functions must also be created in us-east-1.
Lambda@Edge runs your own code at the edge. Here a viewer-response function sets the content security policy and HSTS headers on each response, and it is billed per request.
More Google Slides templatesMore developer workflows templates
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free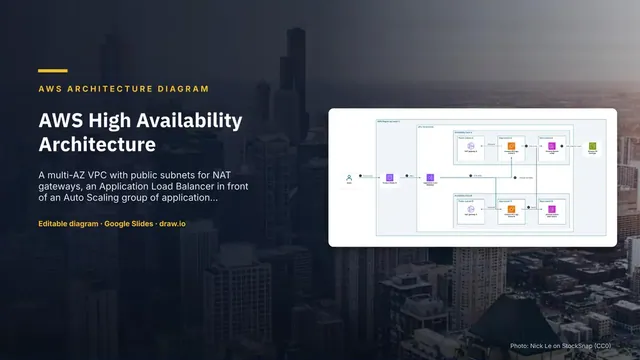
Slides + PowerPoint5 slides
Free










