AWS Three-Tier Web Architecture
Slides + PowerPoint5 slides
Free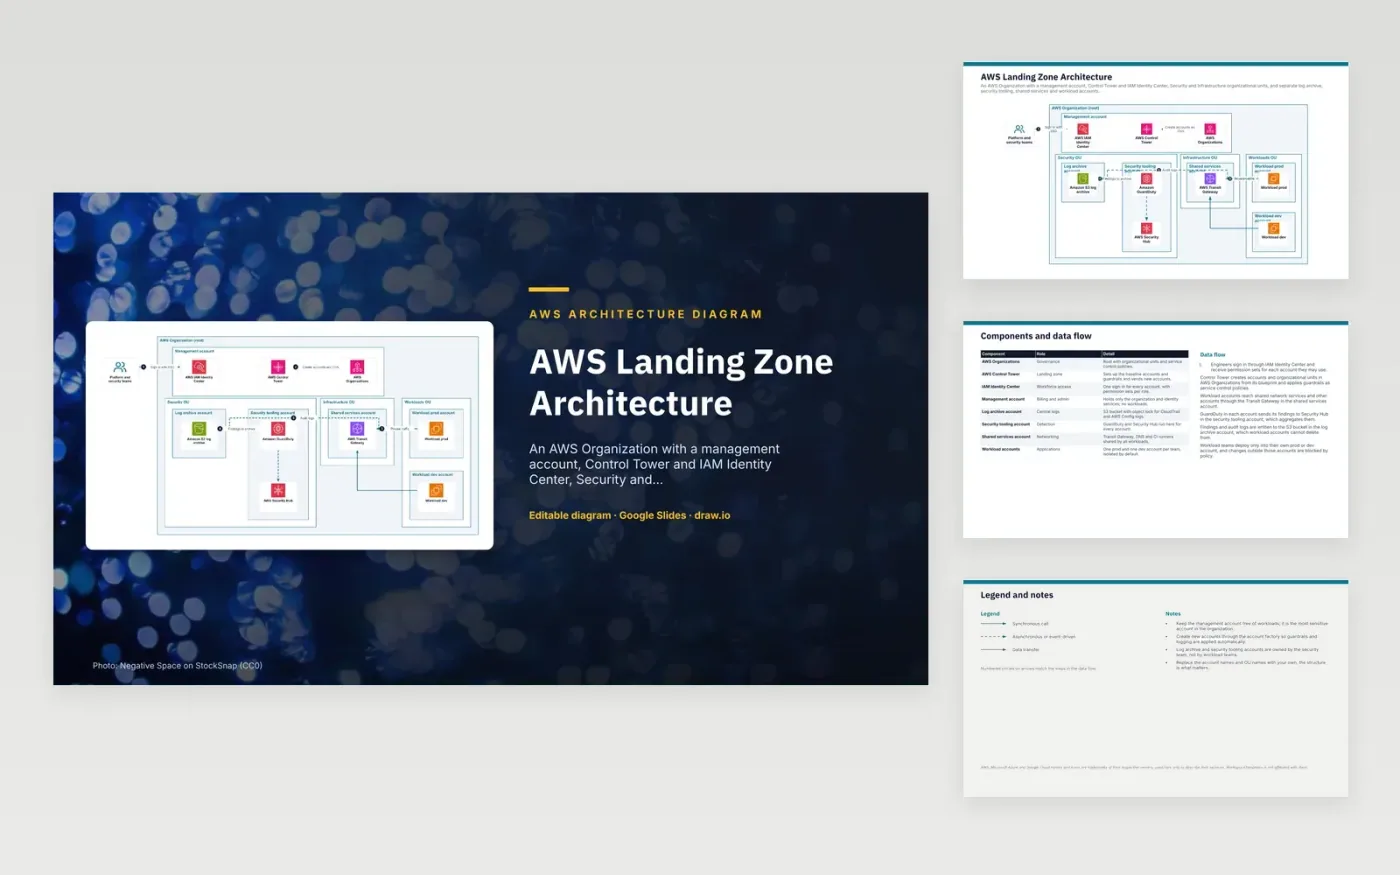
Engineers sign in once through IAM Identity Center and receive permission sets for the accounts they may use. Control Tower builds the baseline from its blueprint, creating accounts and organisational units in AWS Organizations and applying guardrails as service control policies. Workload accounts reach shared network services through the Transit Gateway. GuardDuty in each account sends findings to Security Hub in the security tooling account. Audit logs land in an S3 bucket in the log archive account, which workload teams cannot delete from.
The management account holds only the organisation and identity services, because it is the most sensitive account and should run no workloads. The log archive and security tooling accounts belong to the security team, so a workload team cannot switch off its own logging. New accounts come from the account factory, so guardrails and logging apply from the first day. A company with fewer teams could drop the separate dev accounts and keep the log and security accounts unchanged.
The diagram uses the official AWS architecture icons, each labelled with its service name. AWS, Microsoft Azure and Google Cloud names and icons are trademarks of their respective owners, used here only to describe their services. WorkspaceTemplates is not affiliated with them.
Click Make a copy in Google Slides, then confirm on the Google page. The copy is saved to your own Google Drive.
Rename Platform and security teams, AWS IAM Identity Center, AWS Control Tower and the other boxes inside AWS Organization (root) to your own components, and delete the ones your system does not have.
Rewrite the 6-step data flow and the 8-row components table so they match the arrows you keep.
For the draw.io version, download aws-landing-zone-architecture-diagram.drawio and open it at app.diagrams.net.
The management account is the root of the organisation and controls billing and account creation. Anyone who compromises it can affect every account beneath it. Keeping application code out limits that exposure to the few services it needs.
A service control policy sets the maximum permissions that accounts in an organisational unit can use, even for their own administrators. It can block regions, services or actions across many accounts at once. Control Tower uses these policies for many of its preventive guardrails.
A separate account keeps copies of logs away from the people and workloads that produce them. With S3 object lock enabled, the logs cannot be deleted or changed during the retention period. That makes them usable as evidence after an incident.
More Google Slides templatesMore developer workflows templates
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free










