Azure Hub-Spoke Network Architecture
Slides + PowerPoint5 slides
Free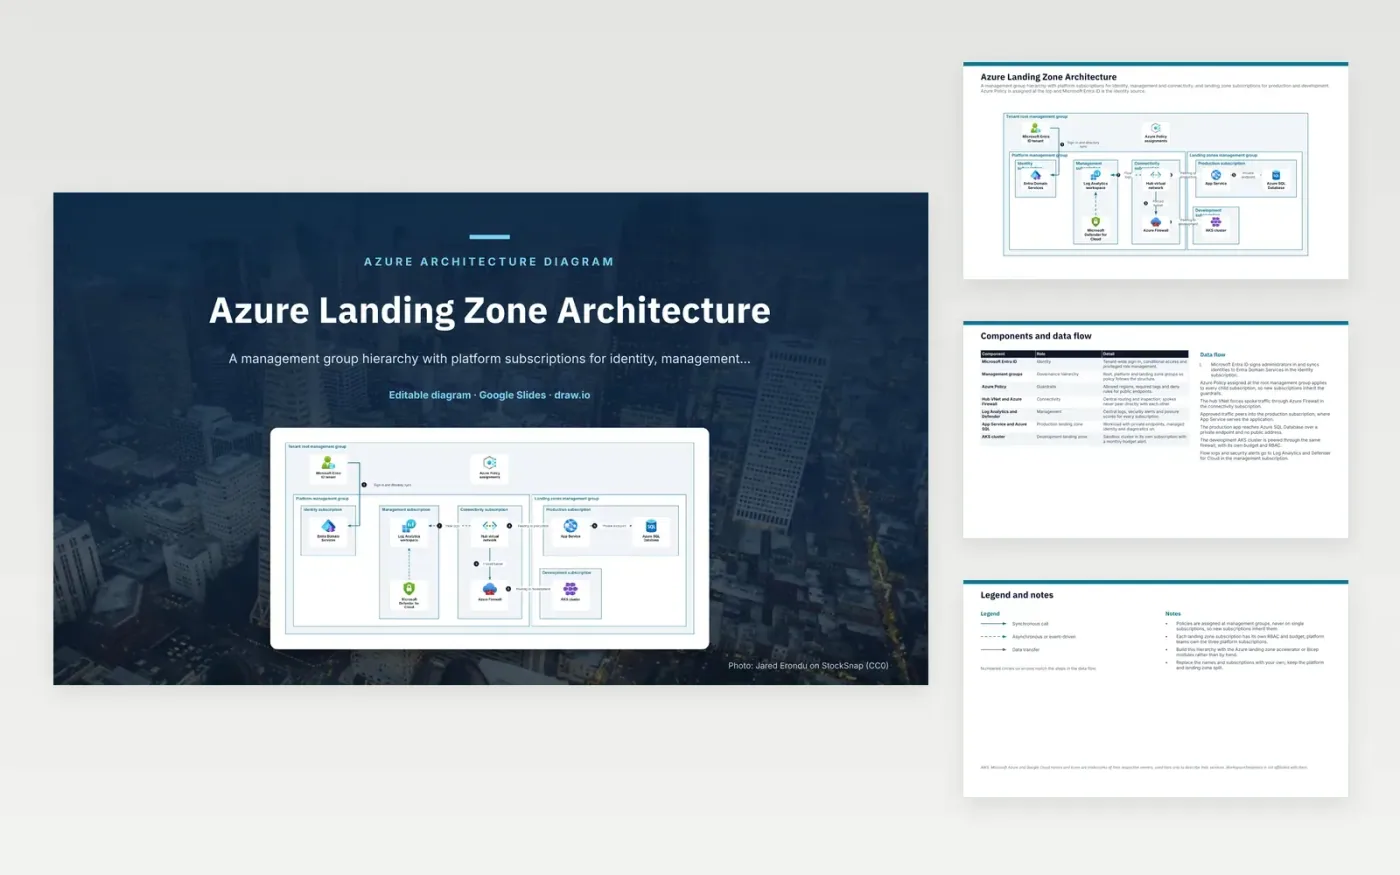
Microsoft Entra ID signs administrators in and syncs identities to Entra Domain Services in the identity subscription. Policies assigned at the root management group apply to every child subscription. Spoke traffic is forced through Azure Firewall in the hub VNet, which lives in the connectivity subscription. Approved traffic peers into the production subscription, where App Service reaches Azure SQL Database over a private endpoint. The development AKS cluster is peered through the same firewall.
Policies belong on management groups, not single subscriptions, so each new subscription inherits the guardrails on day one. Each landing zone subscription has its own RBAC and budget, while platform teams own the three platform subscriptions. Spokes never peer with each other, which keeps the firewall as the only route between them. To adapt it, rename the groups and subscriptions to match your organisation, and build the hierarchy with the accelerator or Bicep modules rather than by hand.
The diagram uses the official Microsoft Azure architecture icons, each labelled with its service name. AWS, Microsoft Azure and Google Cloud names and icons are trademarks of their respective owners, used here only to describe their services. WorkspaceTemplates is not affiliated with them.
Click Make a copy in Google Slides, then confirm on the Google page. The copy is saved to your own Google Drive.
Rename Microsoft Entra ID tenant, Azure Policy assignments, Entra Domain Services and the other boxes inside Tenant root management group to your own components, and delete the ones your system does not have.
Rewrite the 7-step data flow and the 7-row components table so they match the arrows you keep.
For the draw.io version, download azure-landing-zone-architecture-diagram.drawio and open it at app.diagrams.net.
A policy assigned at a management group applies to every subscription under it, including ones created later. New subscriptions therefore inherit the same rules without extra work. Assigning policy to single subscriptions leaves gaps that teams can miss.
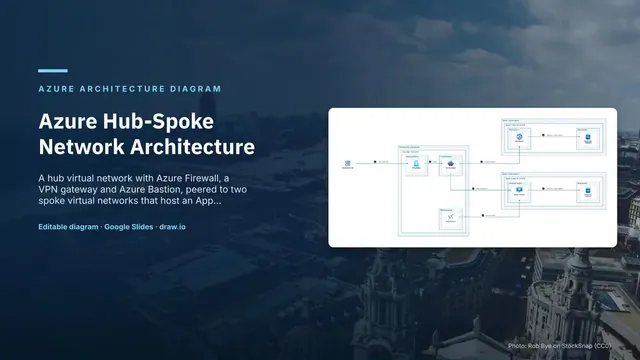
The hub holds shared services such as routing, DNS and Azure Firewall. Spoke networks connect to the hub, so inspected traffic passes one set of controls. Spokes do not peer with each other directly, which keeps routing simple to audit.
Microsoft Entra ID is the cloud identity service that handles sign-in and directory data for the tenant. Entra Domain Services provides managed domain services, such as LDAP and domain join, for legacy applications that cannot use Entra ID directly. Both are part of the identity design.
More Google Slides templatesMore developer workflows templates
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free
Slides + PowerPoint5 slides
Free










