Application Security Review
Docs + Word9 pages
Free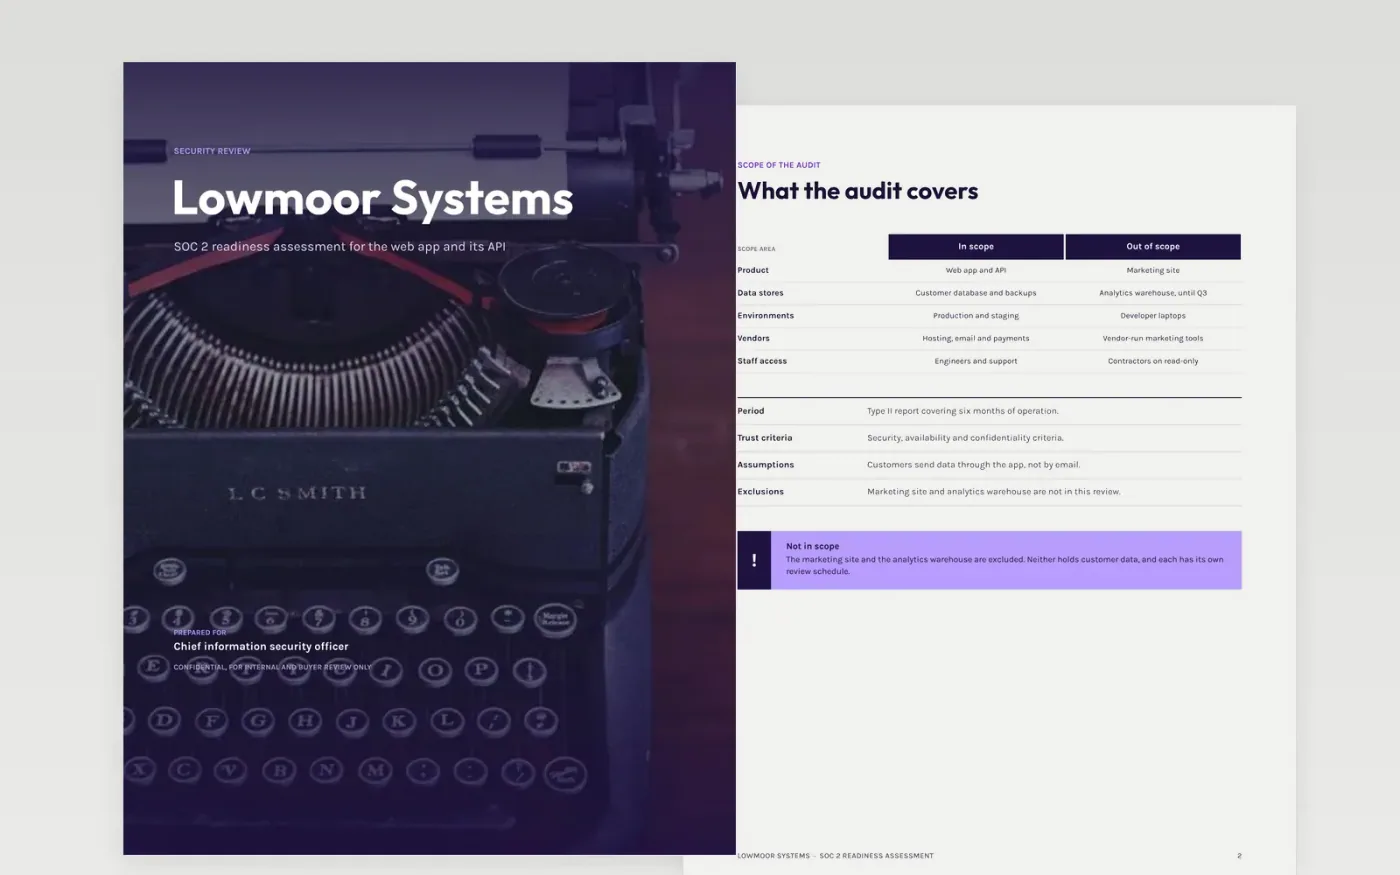
Enterprise buyers ask for SOC 2 evidence long before an audit, and startups often answer with a list of tools rather than controls. This assessment maps current controls to the trust criteria, rates the risks by likelihood and impact, and sets out the findings with owners and deadlines. It moves from scope and criteria to controls, gaps and a dated plan, so security can approve a launch on evidence.
The sample belongs to Lowmoor Systems, a fictional software company with one critical risk and one high finding open. It shows a web app in scope, an analytics warehouse out of scope and a remediation plan with seven-day and 30-day targets. Replace the scope, the controls and the findings with your own, and rate each one on your own scale before sharing it.
Click Make a copy in Google Docs, then confirm on the Google page. The copy is saved to your own Google Drive.
Set the scope with your systems, data stores and vendors, and say plainly what is left out and why.
Map each control to its criterion and attach the evidence, such as a policy or an extract from the log.
Rate each finding on your own scale, and give every high and critical item an owner and a due date.
Delete the guide page, then share the assessment with the security leads or present it to the board.
No. Lowmoor Systems, its people, its controls and every finding and date in the sample are fictional. Replace them with your own evidence before the assessment is shared with a buyer or an auditor.
No. It is a readiness assessment that helps you prepare for an audit. Only a licensed CPA firm can issue a SOC 2 report, and this template does not replace that work.
Refresh it when the architecture changes and re-score findings at each quarterly review. A register that still shows closed gaps as open, or the reverse, is the fastest way to lose a buyer's trust.
More Google Docs templatesMore developer workflows templates
Docs + Word9 pages
Free
Docs + Word8 pages
Free
Docs + Word8 pages
Free
Docs + Word7 pages
Free
Slides + PowerPoint12 slides
Free
Slides + PowerPoint12 slides
Free
Slides + PowerPoint11 slides
Free
Docs + Word7 pages
Free










