Threat Model
Docs + Word8 pages
Free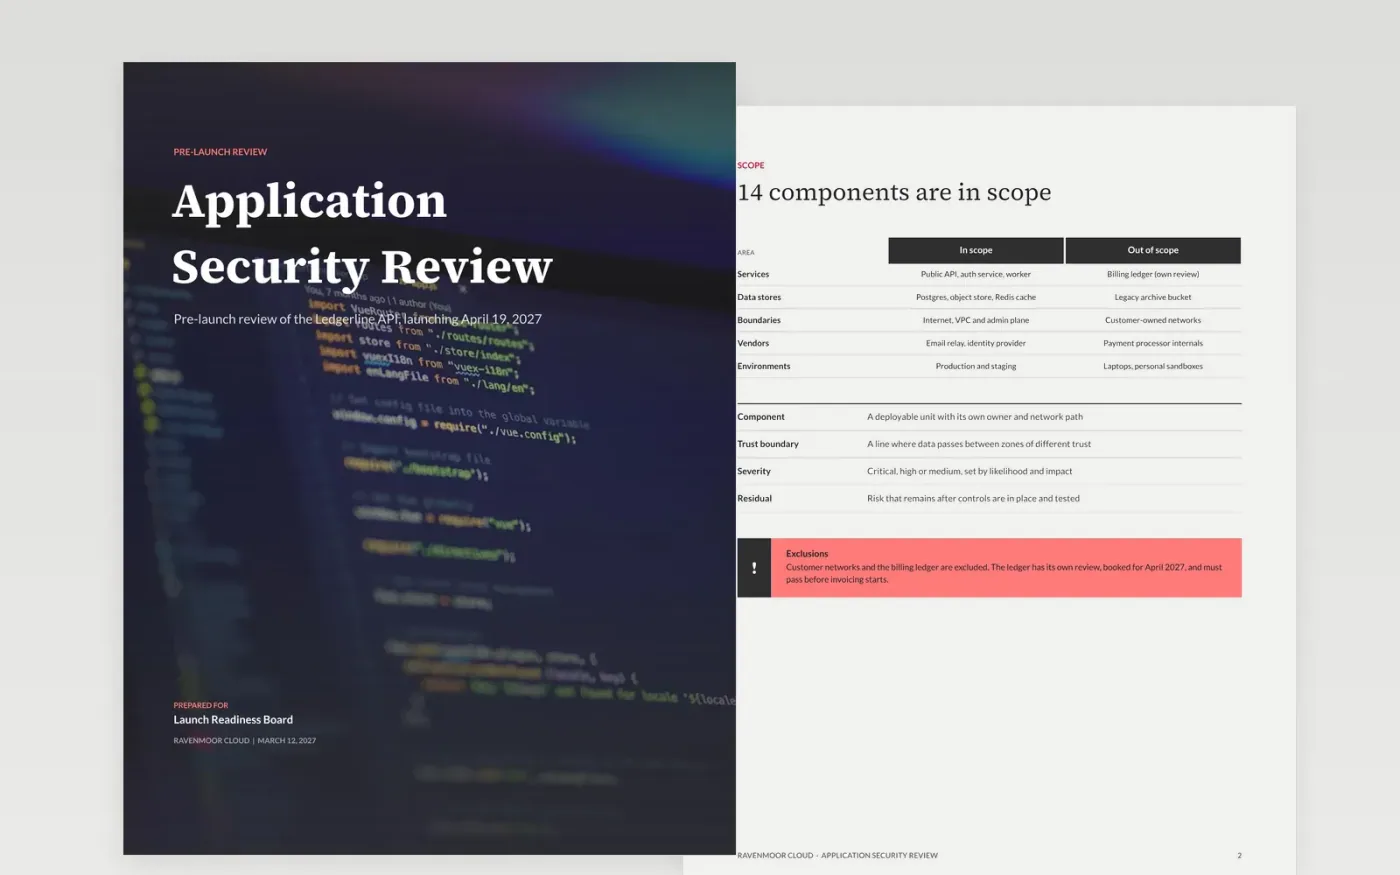
Launch reviews go wrong when the threat model has no diagram, findings follow tool output instead of business impact, and nobody owns the fixes. This template gives security and engineering one document to work through, from scope to a signed decision, across nine designed pages.
The sample reviews a fictional service, the Ledgerline API from Ravenmoor Cloud, with 14 in-scope components, 3 high and 8 medium findings, and a launch decision tied to dated fixes. Replace the components, ratings, owners, due dates and approvers with your own.
Click Make a copy in Google Docs, then confirm on the Google page. The copy is saved to your own Google Drive.
Replace the service name, components and trust boundaries on the cover and scope pages with your own.
Update the authentication, data handling and secrets pages to match what you tested, and re-rate each risk on the heat map.
Enter every finding with its severity, evidence, owner and due date, then fill in the sign-off with the approvers and accepted risks.
Delete the Make it yours guide page, then share the review with your approvers.
Yes. The sample uses critical, high and medium with 7, 30 and 90 day fix targets. Change the labels and the dates to match your policy.
The secrets page has a layered architecture diagram and a request flow. Edit the boxes and labels to draw your own components and trust boundaries.
No. Ravenmoor Cloud, the Ledgerline API, every person and every figure are fictional sample data. Replace all of them with your own before sharing.
More Google Docs templatesMore developer workflows templates
Docs + Word8 pages
Free
Docs + Word8 pages
Free
Slides + PowerPoint11 slides
Free









