
API Documentation
Docs + Word14 pages
Free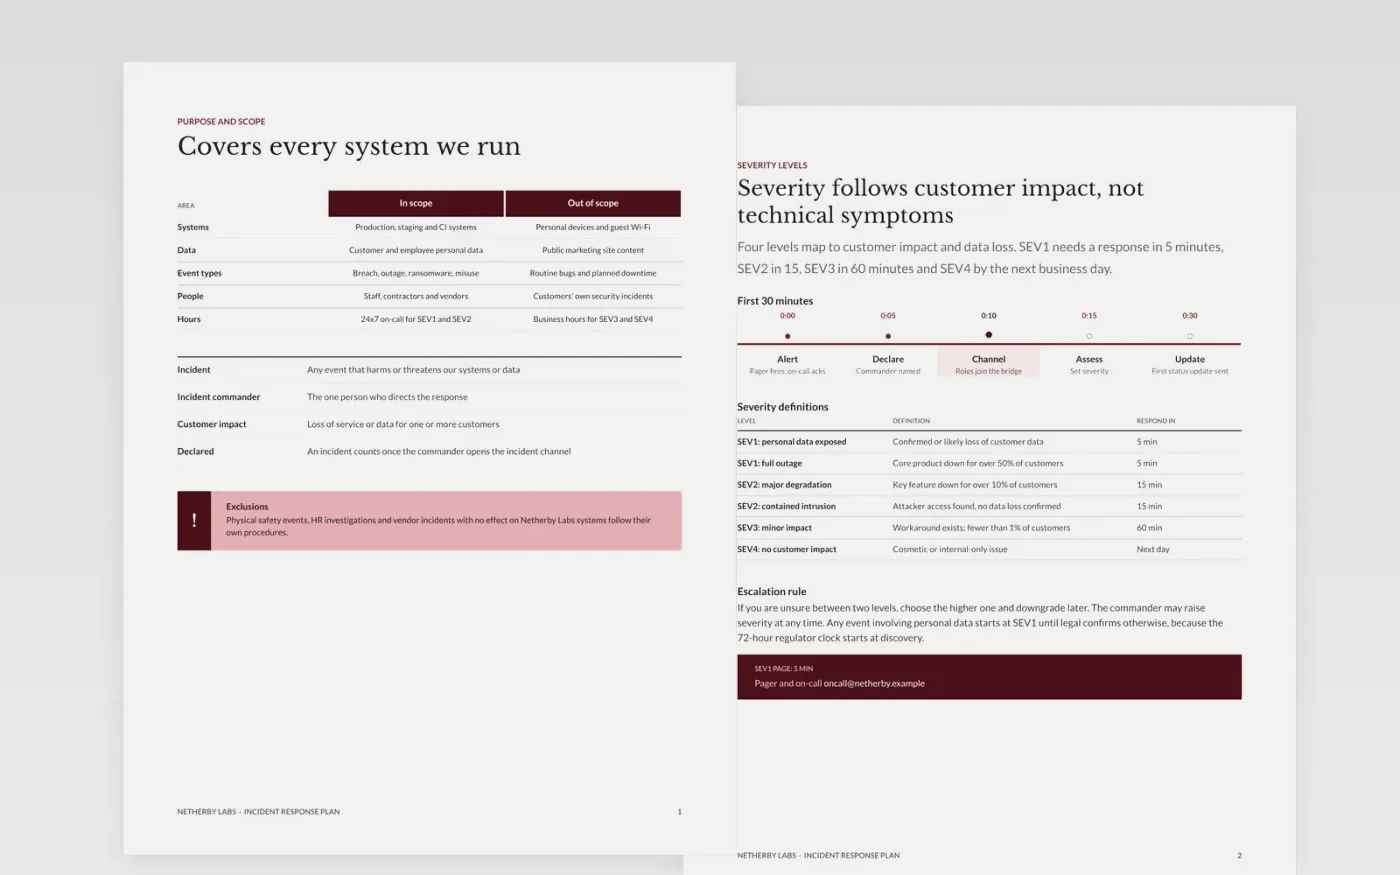
When an incident hits, teams lose minutes arguing about who is in charge and how bad it is. This plan settles that in advance. It defines scope, four severity levels tied to customer impact, a RACI matrix with one accountable person per task, the four response steps, an update schedule by audience and a post-incident review.
The sample is the plan for Netherby Labs, with response times of 5, 15 and 60 minutes and the next business day, updates every 30 minutes for SEV1, and a 72-hour regulator clock. It includes a worked review of a credential leak. Replace the severity table, role holders, contacts, deadlines and scenarios with your own.
Click Make a copy in Google Docs, then confirm on the Google page. The copy is saved to your own Google Drive.
Rewrite the severity table with definitions tied to your customer impact, data loss and revenue, and keep only response times you can meet.
Name the holder and deputy for each role, then add the regulators, customers and insurers you must notify, with each deadline.
Replace the sample review with your own scenarios, and schedule the first tabletop exercise on the review pages.
Delete the guide page, then share the plan with your team or present it at your next on-call briefing.
Scope, severity levels, roles, response steps from declaring to recovering, communication and update cadence, notification duties, a post-incident review and a testing schedule.
Tie them to customer impact and data loss, not to technical symptoms. The sample uses SEV1 to SEV4 with response times of 5, 15 and 60 minutes and the next business day.
No. Netherby Labs, the people and every figure are fictional sample data. Replace them with your own organization, role holders and deadlines before publishing.
More Google Docs templatesMore developer workflows templates
Docs + Word14 pages
Free
Slides + PowerPoint12 slides
Free
Docs + Word17 pages
Free
Docs + Word8 pages
Free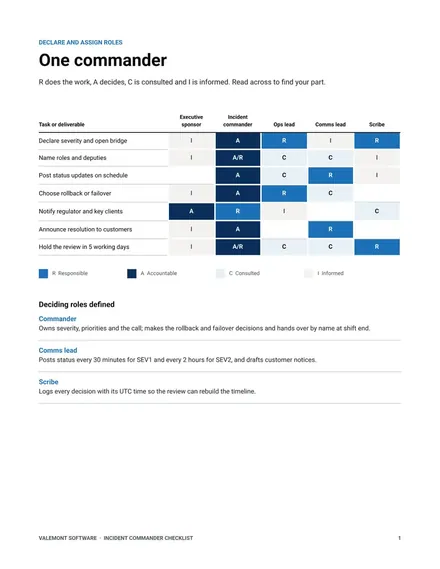
Docs + Word3 pages
Free










